Contracting for athenahealth Calendar Sync: A Claim-to-Obligation Matrix
An athenahealth calendar integration contract checklist should help practice managers turn every relied-upon vendor claim into a written obligation with an owner, acceptance test, ongoing proof, response, and exit action. Review the order form, master terms, statement of work, BAA, data terms, SLA, platform appendices, and termination schedule as one stack; then decide whether to sign, condition, revise, or stop.
What should an athenahealth calendar integration contract checklist accomplish?
It should convert approved requirements and relied-upon evidence into documented operating obligations. Each material commitment needs a responsible party, trigger, proof method, exception response, and exit action. The agreement should not leave essential behavior in a proposal, demonstration, slide deck, or email that is outside the governing contract stack.
When a BAA is applicable, current federal provisions address matters such as permitted uses, safeguards, incident reporting, subcontractors, access, return or destruction, and termination. They do not replace workflow scope, commercial terms, platform behavior, acceptance, support, or service evidence. Review the current 45 CFR 164.504 business-associate contract provisions and HHS sample BAA provisions with authorized reviewers. NIST also treats supplier risk as a lifecycle issue to identify, assess, and mitigate, rather than a one-time questionnaire exercise in SP 800-161 Rev. 1.
Which documents belong in the contract stack?
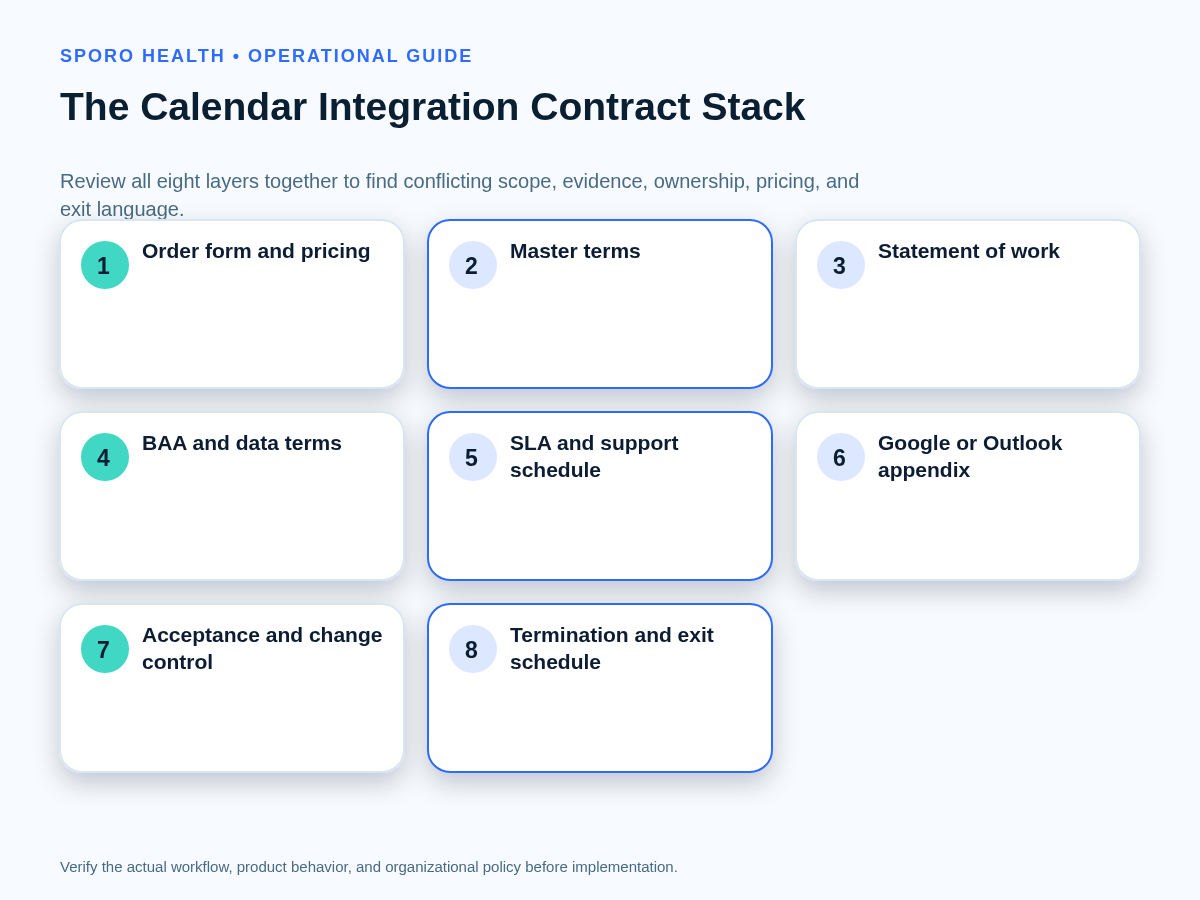
Review eight connected document layers together because one document may narrow, override, or omit another. Create a precedence list, record every incorporated document and version, and require resolution when the same subject receives inconsistent treatment.
| Layer | What it should answer | Common conflict |
|---|---|---|
| Order form and pricing | Purchased scope, term, units, fees | Charges omit support or exit work |
| Master terms | Core rights, warranties, liability, precedence | Broad disclaimers narrow relied-upon claims |
| Statement of work | Workflow, deliverables, roles, dependencies | Demonstrated behavior is not included |
| BAA and data terms | Approved use, safeguards, incidents, disposition | Retention or subprocessor terms disagree |
| SLA and support schedule | Measures, evidence, support, escalation, response | Targets lack an observable measurement point |
| Platform appendices | Google and Outlook scope and exclusions | Parity is assumed but not documented |
| Acceptance and change terms | Tests, defects, approvals, material changes | Acceptance occurs before evidence exists |
| Termination and exit schedule | Continuity, access removal, data, fees, assistance | Exit duties are discretionary or unpriced |
Trace the selected proposal back to the requirements used to write an athenahealth calendar integration RFP. Reconcile the pricing exhibits by using the same scope assumptions applied when you compare calendar integration costs on equivalent scope.
How should the claim-to-obligation matrix work?
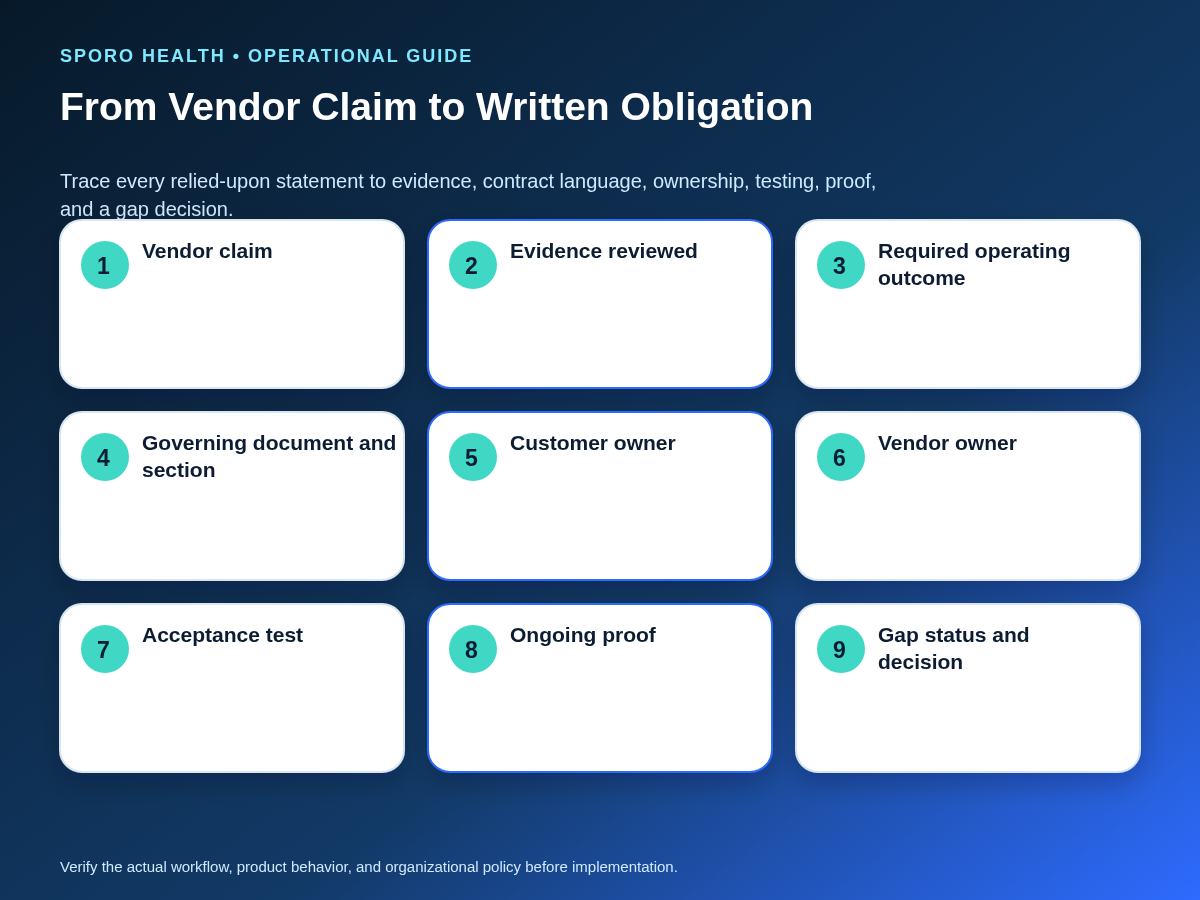
For every material vendor claim, record its evidence, required outcome, governing language, owners, tests, ongoing proof, and unresolved status. Include claims that affected selection even when they appeared only in a demonstration, security response, support conversation, or product page.
| Claim | Evidence | Required outcome | Governing section | Owners | Acceptance | Ongoing proof | Status |
|---|---|---|---|---|---|---|---|
| Example: a canceled appointment will not remain active in the connected calendar | Witnessed test and written response | One final canceled state without an active artifact | SOW and acceptance exhibit | Named customer and vendor roles | Execute and compare both systems | Exception report or reconciliation sample | Resolved, condition, revise, or stop |
Do not translate weak evidence into strong contract language without clarification. First run proof-based vendor due diligence, then attach the evidence identifier to the matrix. A blank governing section means the claim is not yet a contractual obligation.
How should customer and vendor responsibilities be divided?
Assign one accountable owner and one verification method for every recurring or exception task. Shared work is acceptable, but shared accountability without a final owner creates gaps.
| Control | Customer duty to name | Vendor duty to name | Verification |
|---|---|---|---|
| Configuration | Approve workflow and mappings | Implement approved configuration | Versioned configuration record |
| Account administration | Maintain eligible users and calendars | Process supported connection changes | Current connection inventory |
| Permissions | Approve access boundary | Use only approved authorization | Allowed and denied tests |
| Monitoring | Review operational impact | Detect and report service exceptions | Dated reports and alerts |
| Incidents | Protect schedules and coordinate staff | Investigate, restore, and communicate | Incident record and timeline |
| Fallback | Operate the manual procedure | State outage and recovery status | Exercise or incident evidence |
| Reconciliation | Validate operational closure | Provide affected scope and correction evidence | Signed closure record |
| Lifecycle changes | Notify approved changes | Apply and confirm supported changes | Onboarding or offboarding test |
| Escalation | Name decision authority | Name support and executive paths | Tested contact tree |
How should Google Calendar and Outlook scope be written?
Document Google Calendar and Outlook separately rather than assuming identical technical behavior or contractual coverage. Each appendix should identify the actual account, calendar, authorization, transaction, exclusion, and acceptance boundary.
| Worksheet field | Google Calendar appendix | Outlook appendix |
|---|---|---|
| Account and calendar type | Managed user, primary, secondary, or shared | User mailbox, additional calendar, shared mailbox, or Group |
| Authorization path | Client, scopes, consent, delegation if used | Delegated or app-only path and resource scope |
| Read boundary | Named calendars and event states | Named mailboxes, calendars, and event states |
| Write destination | Exact target calendar | Exact target mailbox and calendar |
| Transactions | Create, update, cancel, block, or exclusions | Create, update, cancel, block, or exclusions |
| Direction | One-way or two-way by transaction | One-way or two-way by transaction |
| Notification and recovery | Actual mechanism, renewal, missed-change recovery | Actual mechanism, renewal, lifecycle recovery |
| Acceptance evidence | Positive, negative, recurrence, and revocation tests | Positive, negative, recurrence, and revocation tests |
Platform BAAs and service scope remain separate from the integration vendor’s obligations. Google states that covered customers must accept a BAA for included services and that third-party applications are not covered by the Google Workspace BAA; review its current HIPAA guidance for Google Workspace. Microsoft similarly states that its BAA supports customer compliance but does not make a customer’s use compliant by itself; review the current Microsoft HIPAA and HITECH offering.
What service and incident commitments belong in the package?
Define schedule-risk classes, measurement points, evidence, support paths, restoration duties, reconciliation, escalation, and agreed responses. Do not accept labels such as real time, highly available, or priority support without a measurable definition and a record the practice can review.
HHS notes that an SLA may address availability, reliability, backup, recovery, data return, security responsibility, retention, and disclosure limits, and that it should remain consistent with the BAA. See the current HHS cloud-computing guidance. Translate that principle into calendar-specific commitments:
- Classify failures by potential schedule impact, not only technical severity.
- Name the start and end points of each service measure.
- Require reporting evidence, exclusions, and denominator rules.
- Define restoration and post-restoration reconciliation separately.
- Identify support channels, escalation triggers, and communication owners.
- State the response to repeated misses without inventing unsupported targets.
athenahealth documents appointment schedule, reschedule, cancel, and update notification topics in its event-notification topic guide. If the vendor relies on calendar-platform notifications, require it to explain renewal and missed-message recovery: Google Calendar push channels can expire and notifications are not guaranteed to be complete, while Microsoft Graph webhook subscriptions require lifecycle management and can lose notifications when delivery fails. Use those facts to define schedule-risk service levels around the vendor’s actual design.
How should data use, retention, and subprocessors be addressed?
State the approved purpose, allowed data, prohibited or unresolved secondary uses, retention disposition, subprocessor procedure, and evidence of return or destruction. Align these terms with the approved data-flow design and applicable BAA rather than relying on a broad compliance statement.
- List each data category, source, destination, purpose, and authorized role.
- Resolve whether derived events, mappings, logs, backups, and exports follow different retention clocks.
- Define notice, review, objection, and transition steps for material subprocessor changes.
- Require incident information needed by the practice’s authorized reviewers.
- Specify return, destruction, infeasibility handling, and verification at termination.
The current federal rule requires applicable business-associate contracts to address subcontractor restrictions and return or destruction where feasible. Contract and privacy conclusions depend on the actual parties, configuration, data, and governing law, so this operational checklist is not legal advice.
What should contract change control cover?
Require review before a material change affects the approved workflow. Covered triggers should include integration direction, mappings, permissions, calendar platforms, account types, data use, subprocessors, support, pricing, service evidence, and any feature that changes acceptance results.
For each trigger, define notice, impact information, responsible reviewers, testing, approval authority, effective date, rollback, and emergency handling. The contract should distinguish a vendor platform update from an approved customer configuration change and should not let silence count as approval for a material scope expansion. The operating procedure used to control changes to a live calendar integration can serve as an acceptance test for the proposed contractual process.
What should termination and exit provisions enable?
The practice should be able to stop synchronized writes, preserve schedule continuity, resolve artifacts, remove access, and verify data disposition. Exit language should make the operating sequence possible rather than merely granting a general right to terminate.
- Define who can order a stop and how receipt is confirmed.
- Preserve an authoritative schedule and manual fallback during transition.
- Export required records and mappings in an agreed usable form.
- Classify existing calendar events, recurrence, and orphaned artifacts.
- Remove platform and vendor access, then test for residual paths.
- Document return or destruction, transition assistance, timing, and fees.
Compare the proposed terms with the steps required to plan a controlled calendar integration exit. If the operational exit cannot be executed under the written terms, the package is incomplete.
How should contradictions and omissions be scanned?
Search across the whole stack for the same concept, then record which document controls and what must change. At minimum, scan for:
- Undefined scope or an order form broader than the accepted workflow.
- Retention, deletion, or secondary-use terms that conflict with the BAA or data design.
- Service measures with no observable event, evidence source, or reporting duty.
- Discretionary platform, permission, or subprocessor changes without review.
- Exit work, exports, or artifact cleanup that is optional, unpriced, or ownerless.
- Configuration, monitoring, fallback, reconciliation, or escalation assigned to nobody.
Give each finding a severity, owner, governing documents, required correction, due date, and effect on the signing decision. Do not close a contradiction by choosing the most favorable interpretation without written confirmation.
What should the pre-signature gate decide?
The evidence should produce one of four outcomes: sign, sign with documented conditions, return for revision, or stop. The gate is a decision record, not a meeting note.
| Outcome | Use when | Required record |
|---|---|---|
| Sign | Material obligations, evidence, ownership, and exit are resolved | Approved matrix and final document versions |
| Sign with documented conditions | A bounded gap has an owner, protection, deadline, and consequence | Condition, due date, proof, and authority |
| Return for revision | Language conflicts with evidence or omits a material obligation | Requested edits and affected sections |
| Stop | A critical workflow, data, support, platform, acceptance, or exit gap remains uncontrolled | Reason, evidence, and authorized decision |
Every open condition needs a dated owner and a protective rule that applies before resolution. A critical gap should not be converted into a routine post-signature task merely to preserve the procurement schedule.
Where do current Sporo destinations fit?
Use product destinations as vendor evidence to test, not as substitutes for the final agreement. If Sporo is under consideration, inspect the Sporo Health overview, the current athenahealth and Google Calendar product page, the athenahealth and Microsoft Outlook product page, and the Sporo athenaConnect Marketplace listing. Copy each relied-upon statement into the claim-to-obligation matrix and require the governing document, owner, test, proof, and remedy.
How should buyers use the athenahealth calendar integration contract checklist?
Build the matrices before signature, circulate unresolved items to authorized reviewers, and preserve one dated decision packet. The packet should contain the final document index, contradiction log, platform appendices, responsibility boundary, acceptance evidence, open conditions, and sign, condition, revise, or stop decision. The goal is not a longer contract; it is a contract stack that can be operated, verified, changed, and exited.
Frequently asked questions
- Is a signed BAA enough for an athenahealth calendar integration?
-
No. An applicable BAA addresses specified PHI obligations, but it does not by itself define workflow scope, platform behavior, support evidence, pricing, acceptance, change control, or operational exit procedures.
- Which documents belong in the contract stack?
-
Review the order form, master terms, statement of work, applicable BAA, data and security terms, SLA or support schedule, pricing exhibits, platform appendices, acceptance terms, and exit provisions as one stack.
- What should happen to promises made during a demonstration?
-
Map each relied-upon promise to a governing document and section, owner, acceptance test, ongoing proof, and remedy; otherwise mark it unresolved for authorized review.
- Should Google Calendar and Outlook share one platform appendix?
-
No. Use separate platform appendices because account types, authorization paths, calendar containers, event states, notification mechanisms, exclusions, and acceptance evidence can differ.
- What if the SLA has no measurable evidence?
-
Return it for revision or record a signing condition that names the measure, observation point, evidence, owner, exception rule, escalation trigger, and agreed response.
- Which pre-signature outcome should unresolved critical gaps produce?
-
Use sign, sign with documented conditions, return for revision, or stop. A critical gap with no authorized owner, dated resolution, and protective condition should not be silently accepted.
Sources
- eCFR: 45 CFR 164.504
- HHS: Business Associate Contracts
- HHS: Guidance on HIPAA and Cloud Computing
- NIST SP 800-161 Rev. 1
- athenahealth: Event Notifications Subscription Topics
- Google Calendar API: Push Notifications
- Microsoft Graph: Change Notifications Through Webhooks
- Google Workspace: HIPAA Compliance Guidance
- Microsoft: HIPAA and HITECH Offering